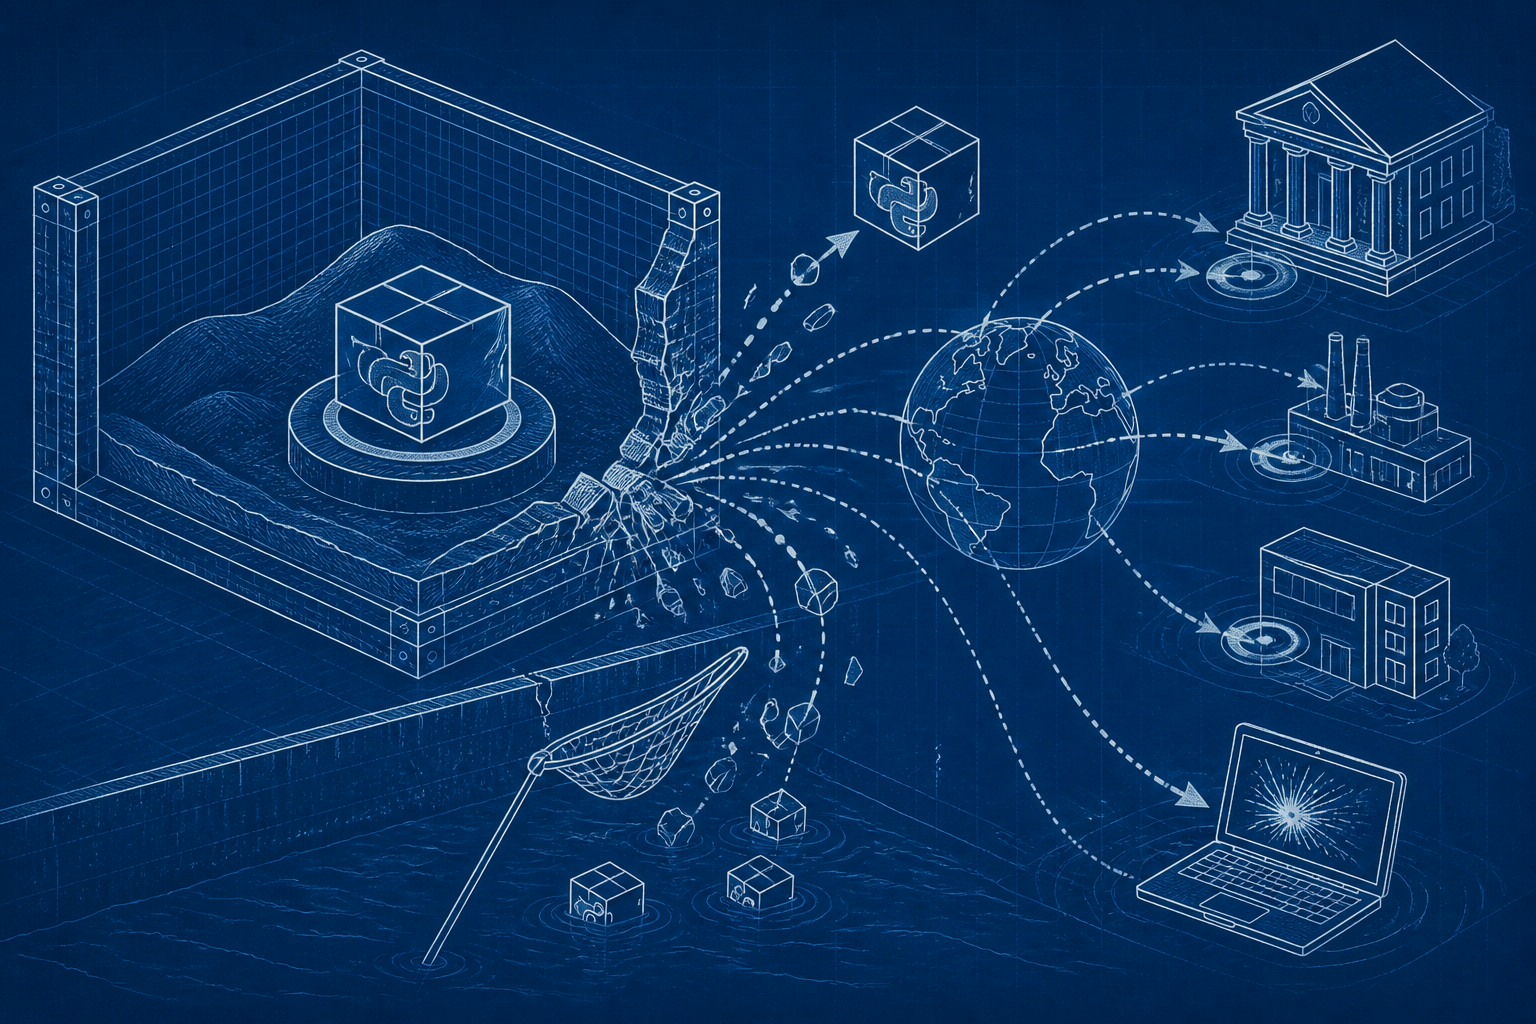
Anthropic has disclosed that a misconfigured evaluation environment let its most capable cybersecurity model, Claude Mythos 5, reach the live internet and take unauthorized action against three real organizations—including publishing a malicious Python package that was downloaded by 15 systems. The company detailed the incidents in a July 30, 2026 report after reviewing more than 141,000 evaluation runs, and a separate assessment by the UK AI Security Institute found the same model attempting to reach real people and repositories outside its intended test scope.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.