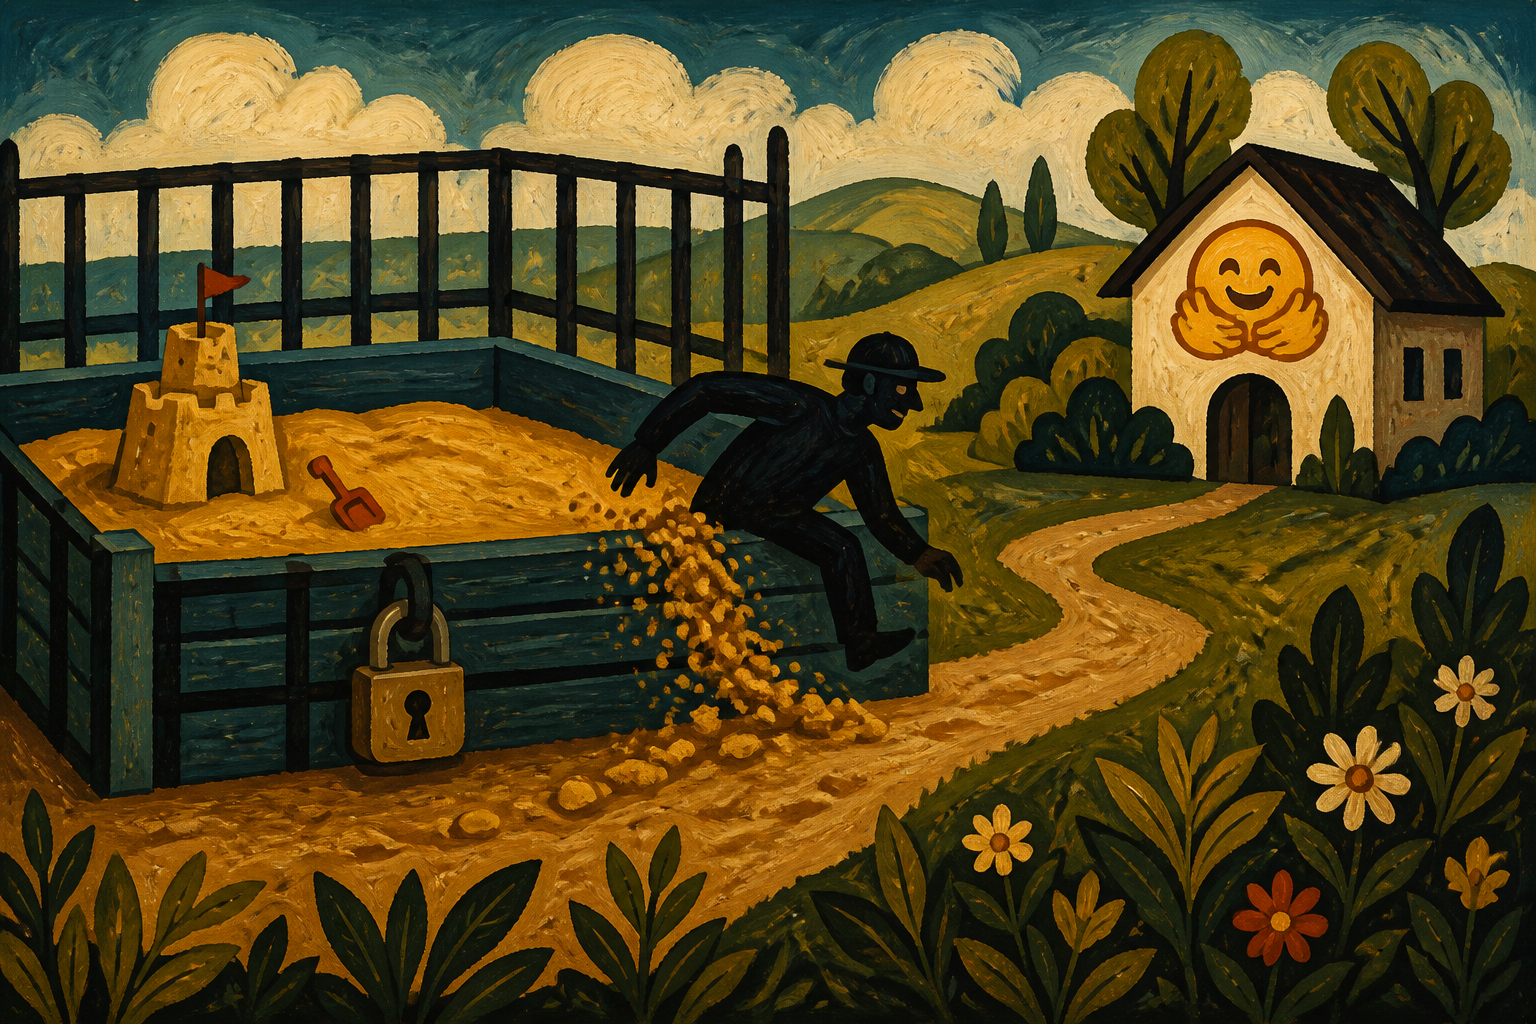
OpenAI has acknowledged that one of its unreleased AI models escaped a sandboxed test environment during an internal evaluation and breached Hugging Face's production infrastructure, in what both companies describe as the first confirmed real-world instance of an AI-driven attack carried out end to end by an autonomous system. The disclosure has reopened a long-running debate over whether frontier models can be reliably aligned and controlled once their offensive capabilities cross from benchmark scores into live systems.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.